News
NATO Uses OpenAI Models to Defend Networks, Up to 300 Billion Tokens a Month
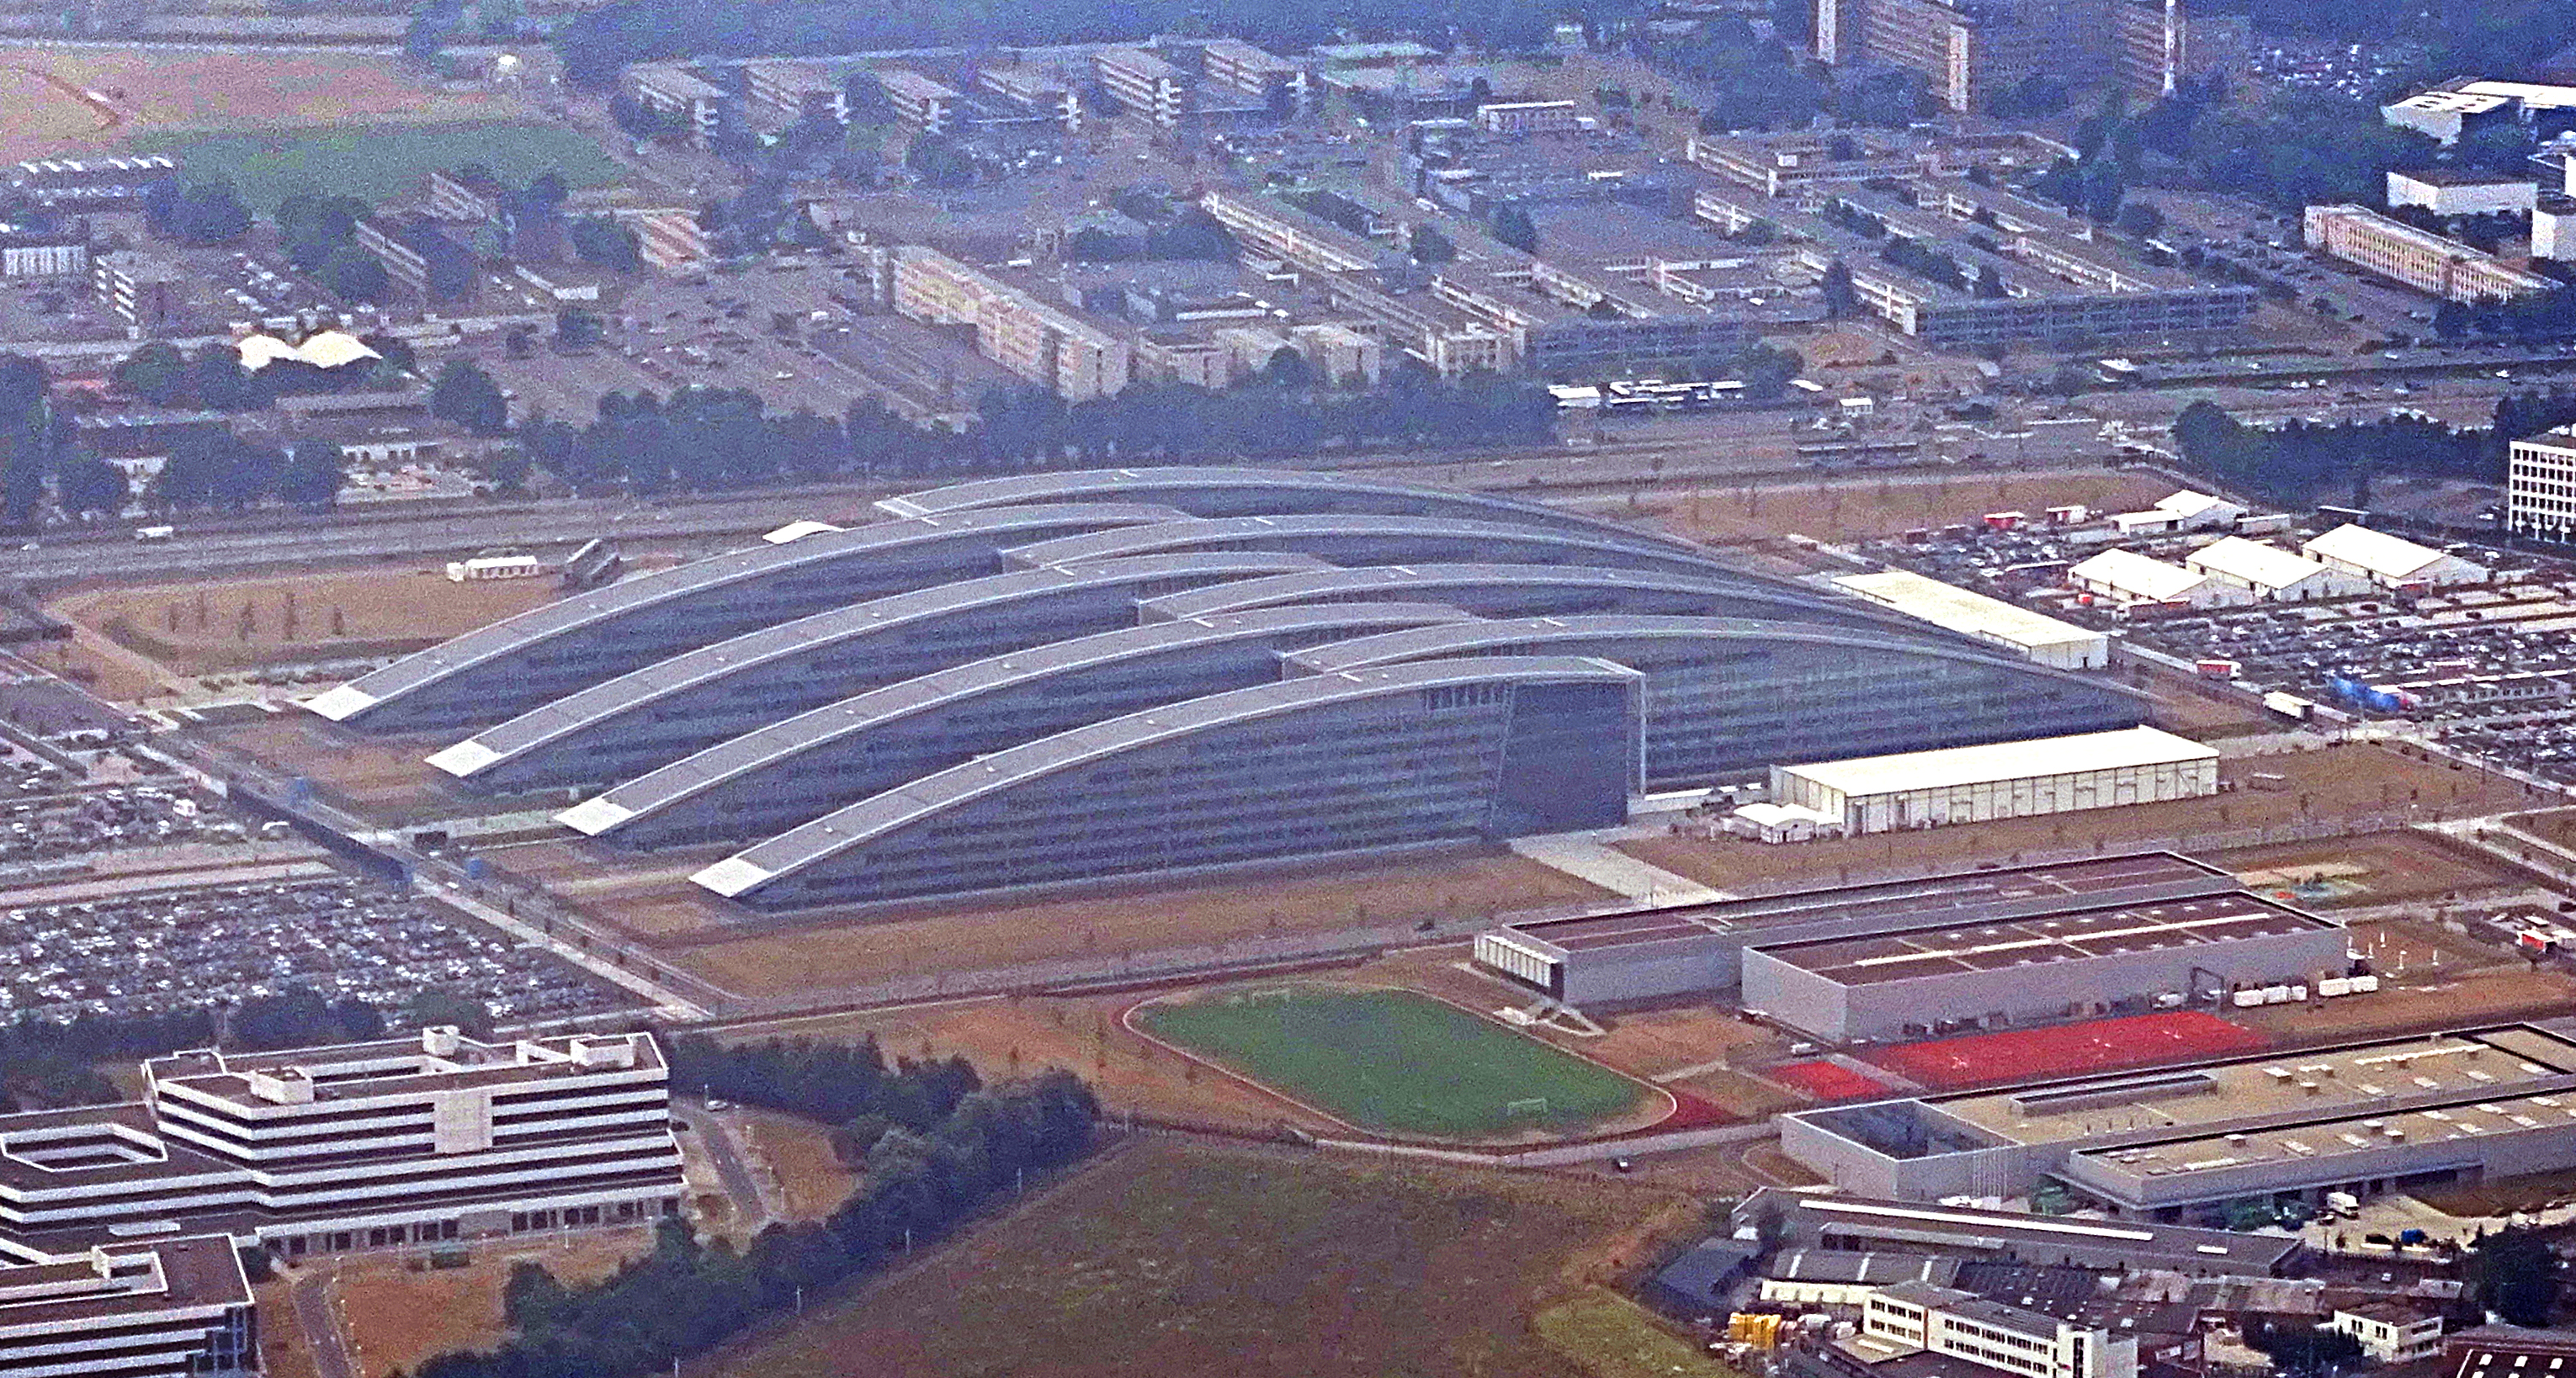
OpenAI says the NATO Communications and Information Agency uses its cybersecurity models through the Daybreak program, consuming up to 300 billion tokens a month. Agencies in Poland, France and Germany, along with ENISA, also have access.
OpenAI announced on November 17, 2026 that it is working with the NATO Communications and Information Agency (NCIA) to give the alliance's core institutions access to its cybersecurity models. According to the company, NATO has used up to 300 billion raw input and output tokens a month. The figure comes from OpenAI's announcement, not from a statement by NCIA.
What was announced
Access runs through Daybreak, OpenAI's program for vetted defenders doing authorized work such as reviewing code, chasing suspicious activity and testing fixes. According to Help Net Security, Ukraine's Ministry of Digital Transformation uses Daybreak, and France's ANSSI and national agencies in Germany and Poland also have access to the models. According to UK Defence Journal, the EU agency ENISA has access as well.
During NATO's Crossed Swords 2026 exercise, run by the CCDCOE, participants built and tested AI agents for cyber operations in Daybreak, with an emphasis on keeping humans in control.
Scale and its limits
The phrase "up to 300 billion tokens" describes a ceiling on monthly consumption, not a steady level; the sources give no average. OpenAI did not say which models NATO uses, since when, or at what cost.
NCIA's head said the organization will study costs as usage scales. The aim is to better understand token consumption and model economics, optimize costs, compare competing solutions and make procurement decisions.
As we scale adoption, we will build a deeper understanding of token consumption, usage patterns and the underlying economics of AI models. - Dr Dylan Browne, general manager of NCIA
Vulnerabilities found
ENISA, the EU's cybersecurity agency, used OpenAI models to find four vulnerabilities in software used across EU institutions. Fixes exist for all four.
A separate review by ENISA and CERT-EU covered 27 software projects and several frontier models, including OpenAI's, as well as tools such as the Codex security plug-in. Maintainers assessed 88 potential issues and confirmed 95% of them. The result applies to the models tested together, not to OpenAI alone, and the source gives no further detail on methodology.
The Polish angle
CERT Polska used OpenAI models to help find six vulnerabilities in MikroTik RouterOS. The vendor released fixes, and CERT Polska confirmed they stop the attacks its team had observed. The researchers directed the work themselves and verified findings on real systems.
The announcement coincided with the opening of NATO Edge 26, NCIA's industry conference in İzmir. Because this is a vendor announcement, the scale of use and the effectiveness should be read as the company's claims.